Showing posts with label obfuscator. Show all posts

Monday, September 21, 2026

Python Obfuscator & Virtualizer

Python Obfuscator: protect the .py files you actually ship

Python is honest to a fault. You hand someone a script and you have handed them the program. A .pyc is not a lock. PyInstaller is a zip with extra steps. uncompyle6, a strings dump, or “paste this into ChatGPT and tell me what it does” will get you most of the way there.

I built Python Obfuscator because I write Python and I take other people’s Python apart. I wanted a tool I would run on my own code before it left the machine.

It parses the file as an AST, then rewrites it. Renames, encrypted literals, mixed boolean-arithmetic, a generated micro-VM (or FSA, or flattened control flow), integrity probes. The output is still Python. It is just a much worse afternoon for anyone who wanted a free copy of your logic.
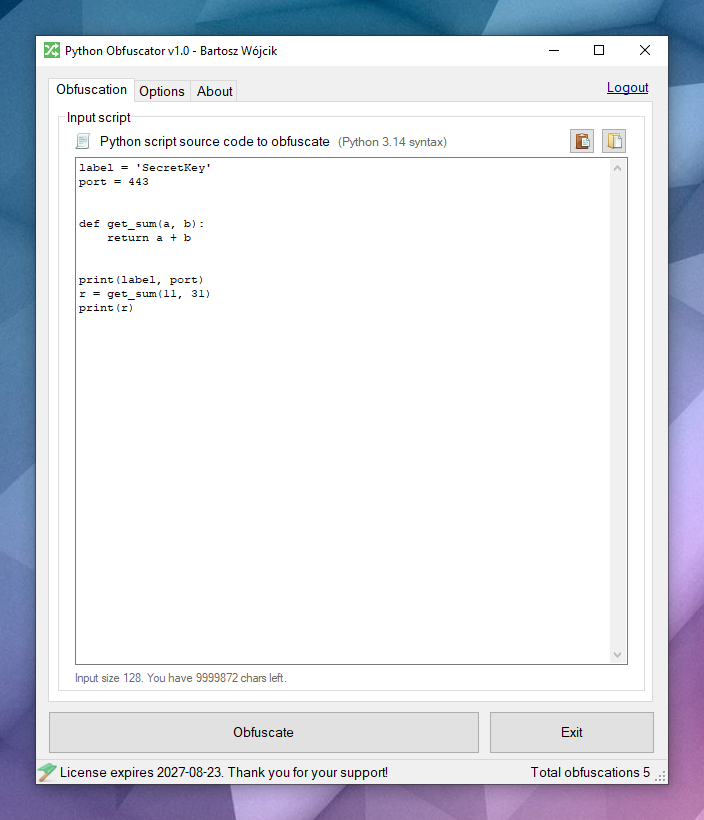
Python Obfuscator main window

That’s the Windows GUI. Same engine as the online tool, the CLI, the SDKs, and the VS Code extension.

Why bother?

If you ship a .py file, the customer already has:

  • every string (URLs, license messages, the “secret” in SecretKey)

  • every function name

  • the control flow, in order

  • anything you thought was “hidden” in a helper module

Obfuscation is not encryption of the universe. It will not stop a funded lab with six months and a debugger. It will stop the cheap reverse: grep, decompile, rename a few symbols, steal the license check, ship it as theirs.

That’s the job. Raise the cost above the value of the script.

What it actually does

You pick the passes. I did not glue this into one “make it messy” button and call it a day — though Check All exists when you mean it.
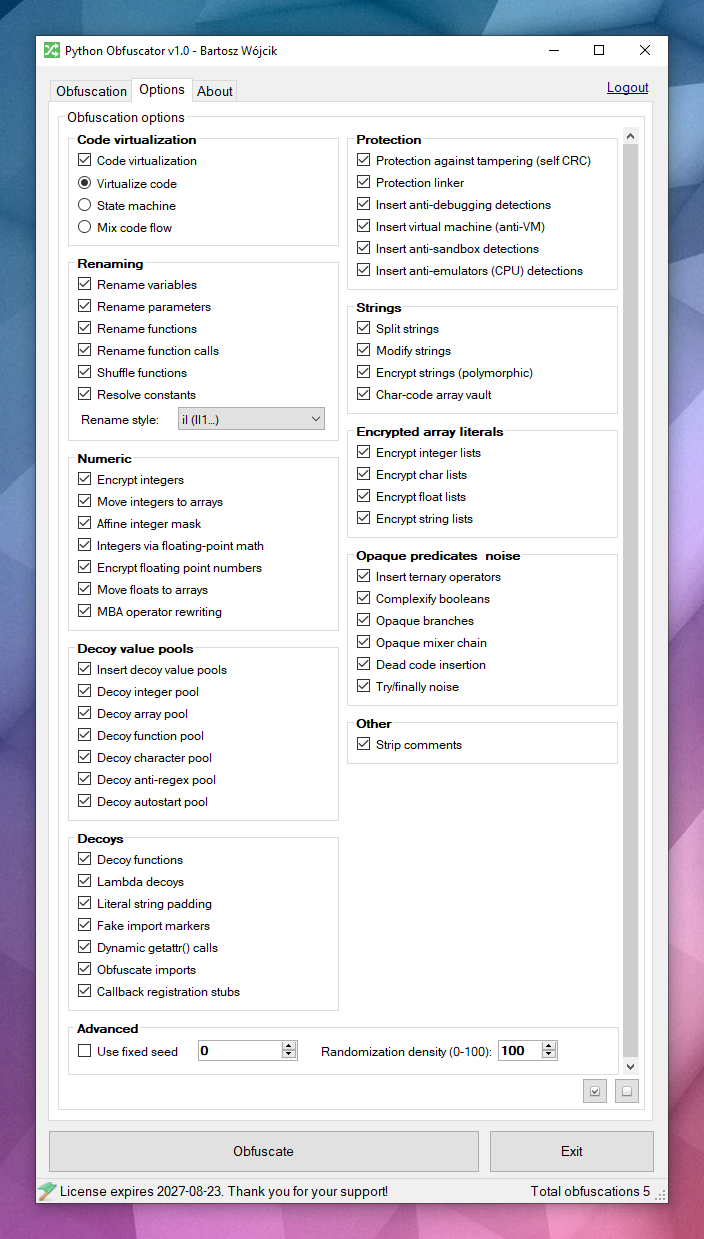
Obfuscation and virtualization options

Code virtualization — one mode at a time:

  • VM — selected statements go into a generated micro-VM with shuffled dispatch. You reverse the interpreter first.

  • FSA — linear blocks become a dual-state automaton. Numeric states instead of top-to-bottom reading.

  • Flat — classic control-flow flattening, lighter than the VM.

Strings — split, mutate, stash fragments in a char-code vault, encrypt with a new polymorphic decryptor every run. Not XOR-with-a-constant. The shape of the loop changes, which is annoying for both grep and the LLM paste workflow.

Numbers — encrypt integers and floats, lift them into arrays, affine masks, mixed boolean-arithmetic (MBA) for operators.

Renaming — variables, parameters, functions, call sites, plus shuffle and constant folding. Styles include il, o0, confusable, hex, homoglyph, mangled.

Noise — dead code, opaque predicates, try/finally junk, decoy functions, fake imports, dynamic getattr calls, random value buckets.

Protection (off unless you turn it on — including --all):

  • Self-defending — a probe fingerprints the module CodeType tree. Patch the file and decryptors start returning garbage.

  • Protection linker — decoy functions and fake calls so a copied fragment still looks like a program. Traps fire if someone edits it or runs a piece alone.

  • Anti-debug / anti-VM / anti-sandbox / anti-emulator — optional, silent exit. They also fire on some developer machines. Leave them off unless you mean it.

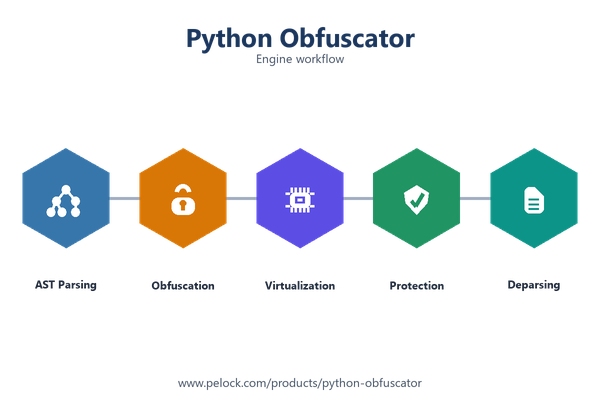
The pipeline in one picture:
Python Obfuscator AST pipeline

AST in. Transforms. Python out. Always run the result on the interpreter you ship with. Python has corners. I hit them too.

Same script, worse file

This is the kind of thing I throw at it:

label = 'SecretKey'
port = 443

def get_sum(a, b):
    return a + b

print(label, port)
r = get_sum(11, 31)
print(r)

It still prints SecretKey 443 and 42. The file you get back does not look like that.
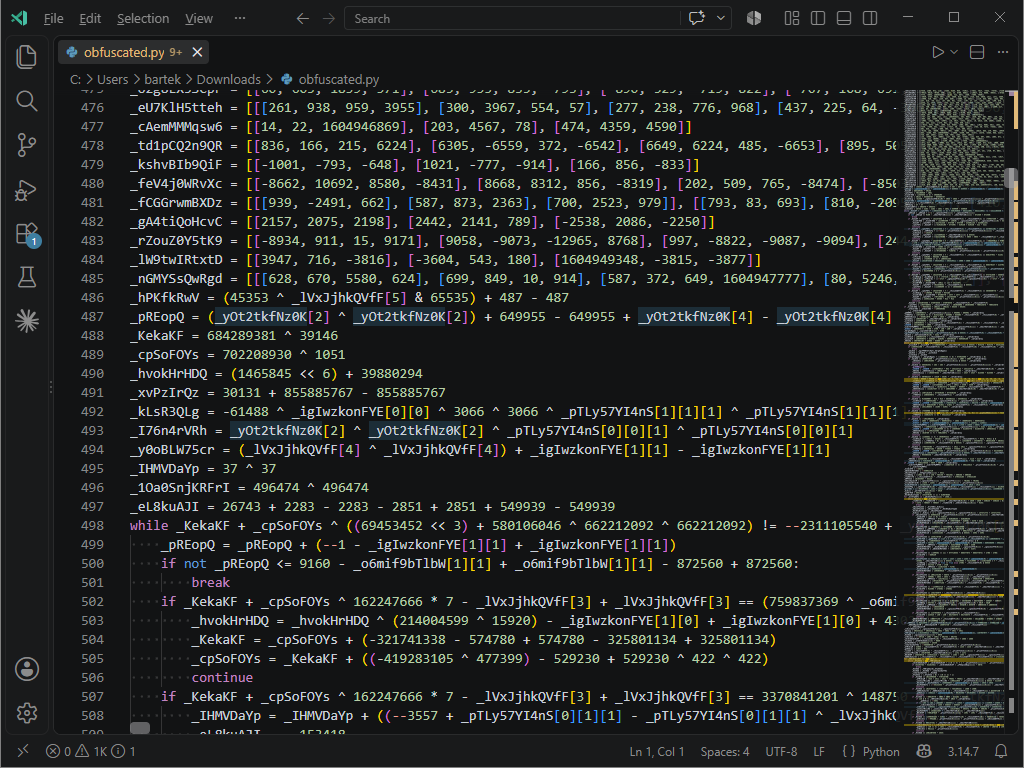
Obfuscated and virtualized Python output

More shots of the UI and CLI: screenshots.

Where people actually use this

Commercial scripts and tools. You sell a .py (or a small package) to customers who are not going to run a private build farm. Obfuscate the release artifact. Keep your working tree clean.

License / activation helpers. The check that talks to your server, the string that is the product name, the expiry message. Encrypt those. Skip the public API you promised not to rename (see the decorator below).

Internal automation that still leaks. A one-off agent on a vendor laptop is still source. If you would be embarrassed to see it on a paste site, run it through the obfuscator.

CI / release jobs. Windows GUI is for poking at options. Linux CLI (and the Web API) is for the Makefile. Obfuscate as a build step, then test the output, then ship.

Trying a setting without installing anything. Paste a snippet into the online tool. Demo mode is enough to see integers-to-arrays, MBA, and string encryption on a short file (1000 characters). Plug in a key and the rest of the pipeline unlocks.

Editing in VS Code / Cursor all day. Right-click, obfuscate, new tab. That is the extension.

Download it

Demo package, Windows installer or zip. CLI works on Windows and Linux (Mono on Linux for the C# command-line client). Internet is required — the heavy lifting is the hosted engine.

Needs .NET 2.0/3.5 on Windows, a few MB of disk, 512 MB RAM. Nothing exotic.
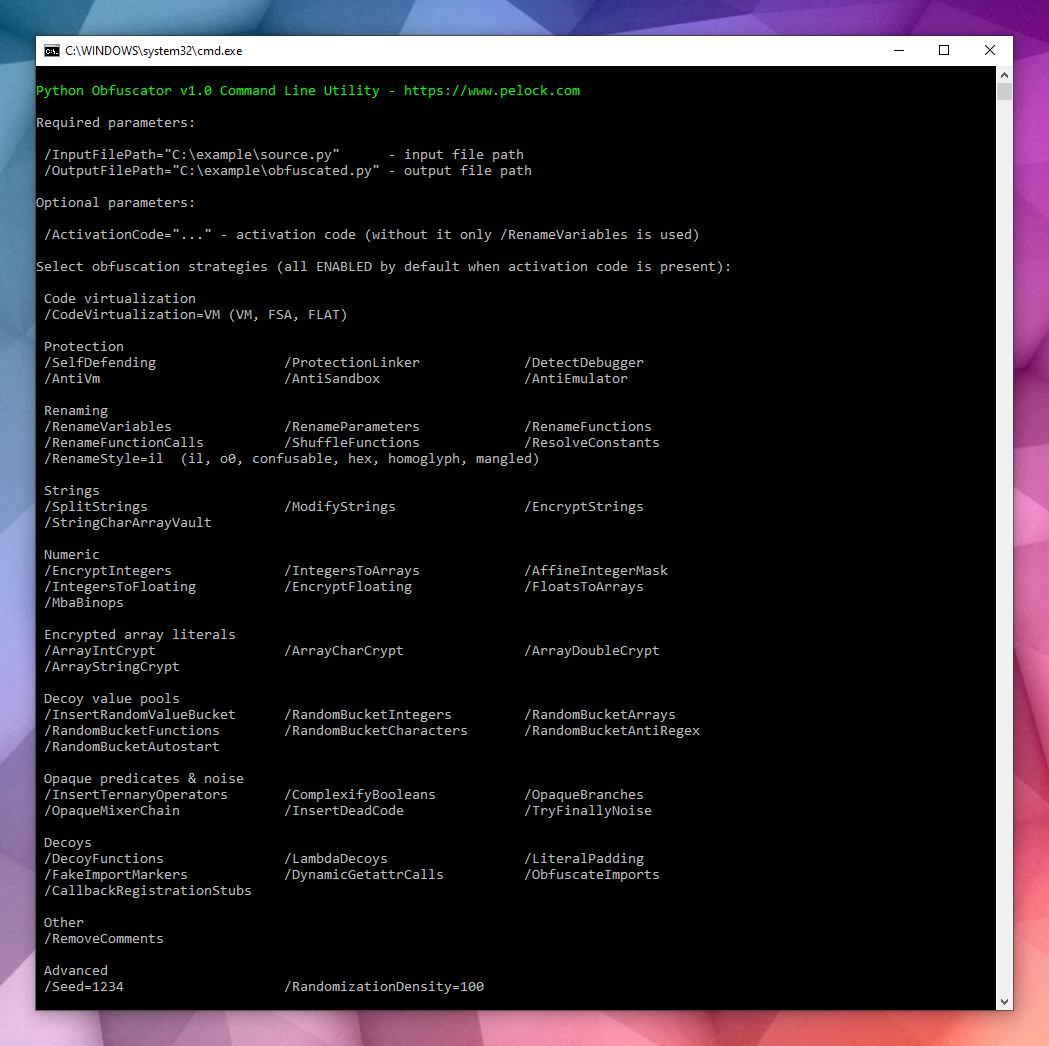
Python Obfuscator CLI on Windows and Linux

Licenses: Personal $149 · Company $499. Empty key = demo.

VS Code (and Cursor)

I live in the editor. So the obfuscator does too.

Right-click a .py → obfuscate. Shortcut is Ctrl+Alt+O (Cmd+Alt+O on a Mac). You get obfuscated.py in a new tab. Settings are the same switches as the website — virtualization mode, renaming style, strings, numbers, protection.
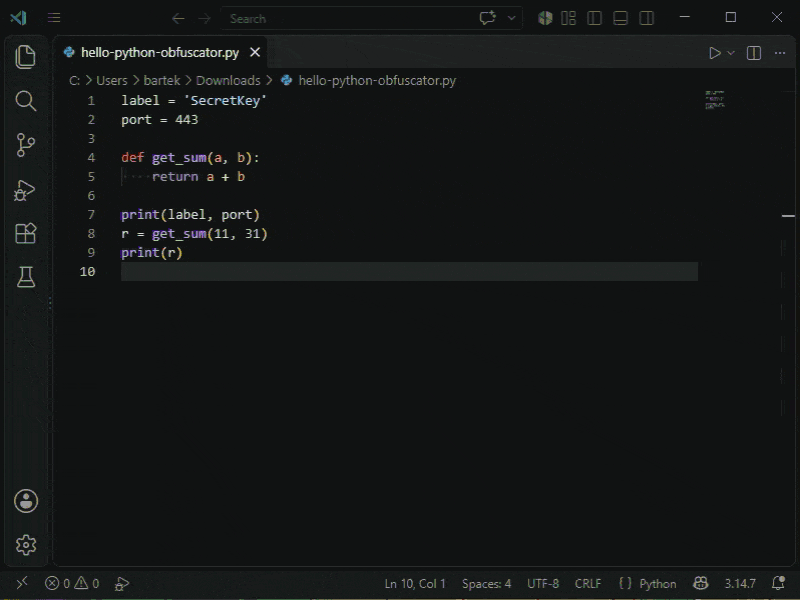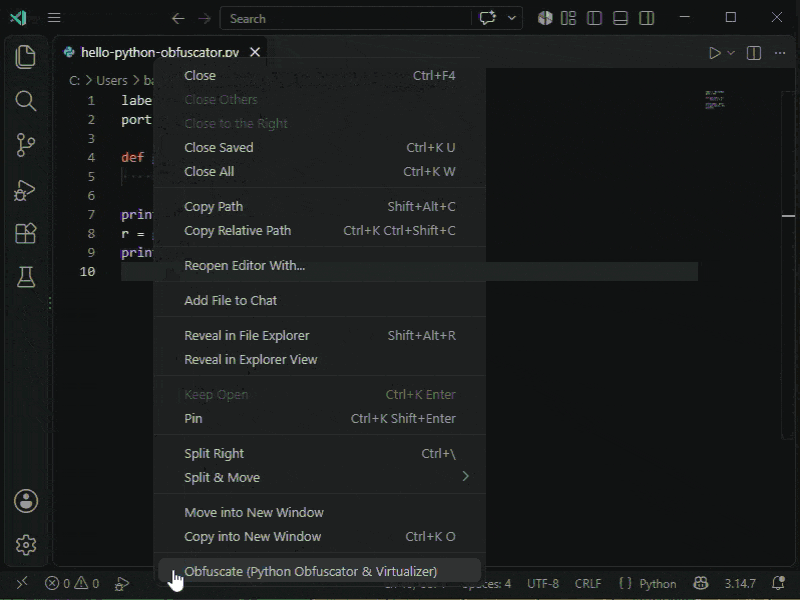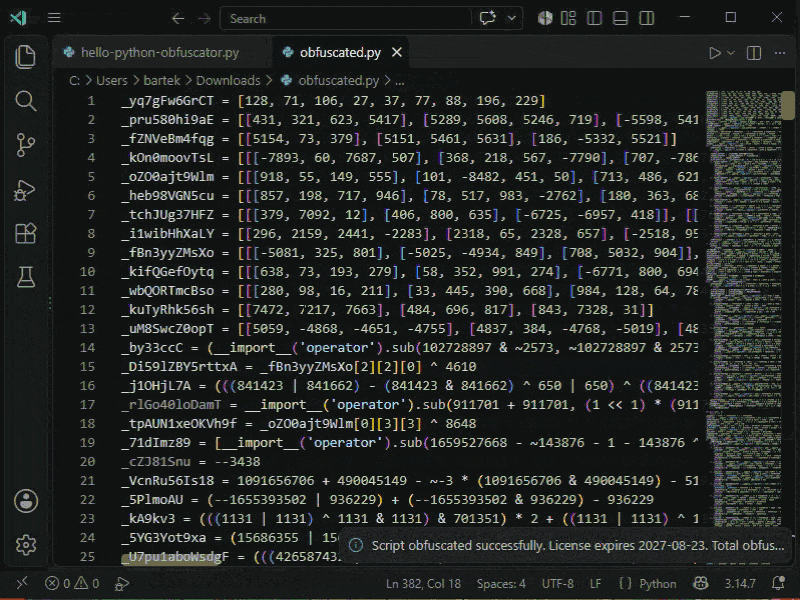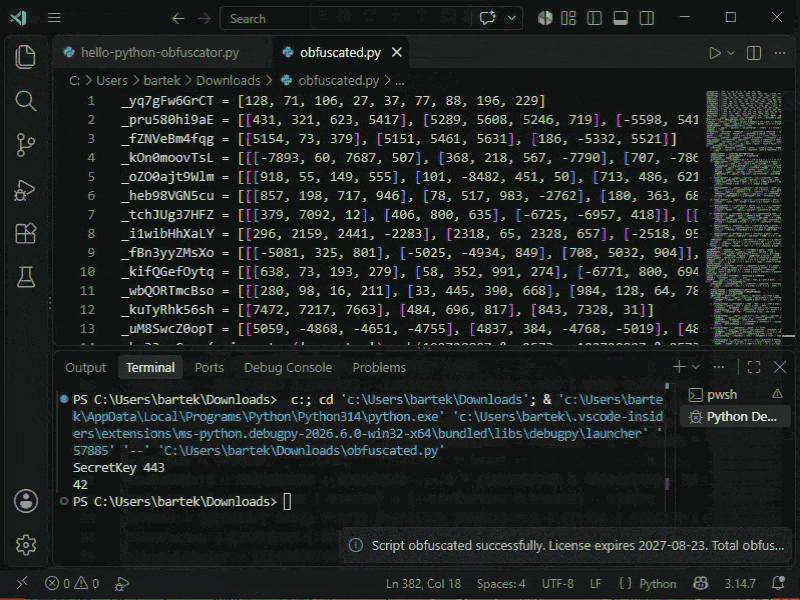
Obfuscating Python inside Visual Studio Code

No key = demo, 1000-character cap. Paste an activation code in Settings (pythonObfuscator) and you get the VM, FSA, flattening, renaming, integrity, the lot.

Web API — put it in a build

Everything the GUI can do is a POST that returns JSON. Docs: pelock.com/products/python-obfuscator/api.

I wrapped it for the languages people actually ask for:

Language

Install

Package

Source

Python

pip install python-obfuscator-virtualizer

PyPI

GitHub

PHP

composer require pelock/python-obfuscator

Packagist

GitHub

JavaScript

npm install python-obfuscator

npm

GitHub

C# / .NET

dotnet add package PELock.PythonObfuscator

NuGet

GitHub

Rust

cargo add python-obfuscator

crates.io

GitHub

Import for the Python SDK is pythonobfuscator. Minimal call:

from pythonobfuscator import PythonObfuscator

client = PythonObfuscator("YOUR-ACTIVATION-CODE")

source = """label = 'SecretKey'
port = 443

def get_sum(a, b):
    return a + b

print(label, port)
r = get_sum(11, 31)
print(r)
"""

result = client.obfuscate_script_source(source)
if result and result["error"] == PythonObfuscator.ERROR_SUCCESS:
    print(result["output"])

You can also pass a file path (obfuscate_script_file(...)). Defaults turn the public strategies on; set booleans yourself if you want a thin pass. code_virtualization is vm, fsa, or flat. Protection flags stay off unless you set them.

Each GitHub repo has a full example with every public flag. I got tired of “which boolean does what.”

login() is there if you only want to check demo / expiry / usages_total / string_limit without obfuscating.

Leave some functions alone: the decorator

You cannot virtualize everything. A handshake string that a test asserts on. A public class name you promised. A function someone monkeypatches.

Python already has a way to mark that. I shipped a tiny package so you can write it in source.

pip install python-obfuscator-decorator

Import name is obfuscator. You only need the package to run the original file. The obfuscator reads @obfuscator.skip off the AST, applies the skip, then strips the decorator and any leftover import obfuscator. The file you ship does not depend on this package.

import obfuscator


@obfuscator.skip(obfuscator.ENCRYPT_STRINGS, obfuscator.CODE_VIRTUALIZATION)
def handshake(secret: str) -> str:
    return secret


@obfuscator.skip()
class LicenseCheck:
    def verify(self) -> bool:
        return True

What the arguments mean:

  • ENCRYPT_STRINGS — keep that literal readable (no string encryption on that construct).

  • CODE_VIRTUALIZATION — skip VM, FSA, and flatten on that function or class.

  • Bare @obfuscator.skip() or @obfuscator.skip — don’t touch this construct at all.

  • String keys work: @obfuscator.skip("encrypt_strings").

  • A skip on a class covers nested methods.

What it will not do: module-level statements have no decorator. Lambdas neither. Don’t skip rename on a function and then expect callers to keep the old name after you renamed everything else.

If you write about it, I’ll send you a key

I do this for my other tools. Write a post, tweet it with #python #obfuscator #obfuscation, send a real bug, or a skip/obfuscation idea with a snippet attached. Email me. If it’s not spam, you get a code.

Try it:

Test the output. Then ship.

Bartosz Wójcik

Wednesday, July 29, 2026

PowerShell Obfuscator & Virtualizer - How to Protect PowerShell Scripts

Looking for a PowerShell obfuscator that can protect .ps1 source without turning your automation into a maintenance nightmare? In this post I explain why I built PowerShell Pro Obfuscator, how PowerShell script obfuscation works in practice, and what you get before vs after.

Why obfuscate PowerShell scripts?

PowerShell is great for automation on Windows and Linux. The problem is distribution: a .ps1 file (or a module) is usually plain text. Anyone with file access can open it, search for passwords and API keys, copy your logic, or patch a license check in minutes.

There is no real “compile to binary” step that hides intent the way native apps sometimes do. If your script is the product, you need PowerShell script protection — not security theater, just a higher cost of casual reading and editing.

That is why I built PowerShell Pro Obfuscator: a dedicated tool to obfuscate PowerShell .ps1 files with renaming, encryption, control-flow transforms, virtualization, and runtime checks.

PowerShell Pro Obfuscator — PowerShell obfuscator GUI

What is PowerShell Pro Obfuscator?

PowerShell Pro Obfuscator is my PowerShell obfuscator / virtualizer for proprietary scripts. It:

  • Parses .ps1 source into an AST

  • Applies selectable obfuscation passes

  • Emits a new protected PowerShell script

I ship the same engine as a Windows GUI, a command-line PowerShell obfuscator for Windows and Linux (useful in CI), plus an online tool and API.

PowerShell obfuscation options

You can keep protection light (rename + encrypt strings) or turn on heavier layers when the script matters more.

PowerShell obfuscation techniques I use

Polymorphic string and number encryption

People grep for URLs, keys, and messages first. I encrypt strings and integers so each build looks different, and I add decoy noise. At runtime the script still decrypts to the same values — the file on disk is just harder to read.

Code virtualization for PowerShell

Selected statements can be lifted into a small random VM (shuffled opcodes, decoy cases, obfuscated dispatcher). Analysts then face a virtual machine instead of plain PowerShell lines. I treat this as optional; it costs more CPU than simple renaming.

Finite-state automata (FSA) transforms

Linear code is easy to follow. FSA obfuscation rewrites blocks into state machines with shuffled handlers and decoy paths, so control flow no longer reads top-to-bottom like a tutorial.

Anti-debugging in obfuscated PowerShell

I insert probes for attached debuggers, breakpoints, and common debug / trace preferences. If a check fires, the script can exit silently — useful against casual interactive analysis.

Self-integrity checks

A bootstrap check verifies the on-disk script still matches the obfuscated build. Decryptors depend on a tamper key, so a casually patched .ps1 often returns garbage instead of plaintext.

Before and after PowerShell obfuscation

Before — obvious intent:

function Get-Greeting {
    param([string]$Name)
    Write-Host "Hello World from $Name!"
}
Get-Greeting "PowerShell Pro Obfuscator"

After — same idea, much harder to skim (real excerpt, truncated):

$script:_HnJTskg = 0
$jwNTQ = 297 * 400 + 36
$x4e8bfda = [Math]::Abs($jwNTQ - 8074)
function gnJjzMCN3V8P {
    param([int]$slot, [int]$salt, [int]$guard)
    if (-not ((Get-Variable -Name _HnJTskg -Scope Script -ErrorAction SilentlyContinue).Value)) { return '' }
    $d = @(46866, 46865)
    $r = ''
    for ($i = 0; $i -lt $d.Length; $i++) {
        [long]$v = [long]$d[$i]
        # ... polymorphic decode loop ...
        if ([long]$v -ge 0 -and [long]$v -le 0xFFFF) { $r += [char][int][long]$v }
    }
    return $r
}
...

If you only had the obfuscated file, would you still spot a simple greeting helper?

Obfuscated PowerShell script example

How this PowerShell obfuscator works

Pipeline in short: parse → transform → emit .ps1.

Passes can include renaming, control-flow flattening, FSA, VM virtualization, polymorphic encryption, noise, integrity probes, a protection linker, and anti-debugging. Always test the output in your real PowerShell host — grammar and hosting edge cases still exist.

PowerShell Pro Obfuscator pipeline

CLI: obfuscate PowerShell scripts in CI

For build servers I use the command-line client on Windows or Linux: obfuscate the release script, run smoke tests, then publish the protected .ps1.

PowerShell obfuscator command line

Try PowerShell Pro Obfuscator

If you need to obfuscate PowerShell scripts, protect proprietary .ps1 logic, or add virtualization and integrity checks without reinventing the pipeline, start here:

Product page: PowerShell Pro Obfuscator — obfuscate & protect PowerShell scripts

Questions? Contact me.

Wednesday, June 10, 2026

Java Obfuscator for Maven

JObfuscator is a modern Java obfuscator. It operates at the source code level & employs a range of obfuscation techniques to protect the code against decompilation, reverse engineering, and LLM analysis.

Java Obfuscator

How to use Java obfuscator?

The easiest way to use JObfuscator is via Maven pre-compiler plugin. Follow the steps to add JObfuscator to your Maven build workflow:

Step 1 - integrate into your Maven workflow

Add the plugin, annotation library and its settings to your application pom.xml, minimal configuration:


<?
xml version="1.0" encoding="UTF-8"?>

<project xmlns="http://maven.apache.org/POM/4.0.0"
         xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
         xsi:schemaLocation="http://maven.apache.org/POM/4.0.0 https://maven.apache.org/xsd/maven-4.0.0.xsd">
  <modelVersion>4.0.0</modelVersion>
  <groupId>com.example</groupId>
  <artifactId>my-app</artifactId>
  <version>1.0.0-SNAPSHOT</version>

  <properties>
    <project.build.sourceEncoding>UTF-8</project.build.sourceEncoding>
    <maven.compiler.release>11</maven.compiler.release>
    <jobfuscator.apiKey><!-- YOU-API-HERE or leave empty for DEMO VERSION --></jobfuscator.apiKey>
    <jobfuscator.version><!-- e.g. 1.0.3 --></jobfuscator.version>
  </properties>

  <dependencies>
    <dependency>
      <groupId>com.pelock</groupId>
      <artifactId>jobfuscator-annotations</artifactId>
      <version>${jobfuscator.version}</version>
      <scope>provided</scope>
    </dependency>
  </dependencies>

  <build>
    <plugins>
      <plugin>
        <groupId>com.pelock</groupId>
        <artifactId>jobfuscator-maven-plugin</artifactId>
        <version>${jobfuscator.version}</version>
        <executions>
          <execution>
            <goals>
              <goal>obfuscate-sources</goal>
            </goals>
            <phase>generate-sources</phase>
          </execution>
        </executions>
        <configuration>
          <apiKey>${jobfuscator.apiKey}</apiKey>
          <enableCompression>true</enableCompression>
          <mixCodeFlow>true</mixCodeFlow>
          <renameVariables>true</renameVariables>
          <renameMethods>true</renameMethods>
          <shuffleMethods>true</shuffleMethods>
          <intsMathCrypt>true</intsMathCrypt>
          <cryptStrings>true</cryptStrings>
          <stringSplit>true</stringSplit>
          <intsToArrays>true</intsToArrays>
          <dblsToArrays>true</dblsToArrays>
          <dblsMathCrypt>true</dblsMathCrypt>
          <stringCharVault>true</stringCharVault>
          <intsFromDoubleMath>true</intsFromDoubleMath>
          <opaqueMixerChain>true</opaqueMixerChain>
          <complexifyBooleans>true</complexifyBooleans>
          <tryFinallyNoise>true</tryFinallyNoise>
          <selfCheck>true</selfCheck>
          <arrayIntCrypt>true</arrayIntCrypt>
          <arrayCharCrypt>true</arrayCharCrypt>
          <arrayDoubleCrypt>true</arrayDoubleCrypt>
          <arrayStringCrypt>true</arrayStringCrypt>
          <selfCheck>true</selfCheck>
        </configuration>
      </plugin>
      <plugin>
        <groupId>org.apache.maven.plugins</groupId>
        <artifactId>maven-compiler-plugin</artifactId>
        <version>3.13.0</version>
        <configuration>
          <release>${maven.compiler.release}</release>
        </configuration>
      </plugin>
    </plugins>
  </build>
</project>


Step 2 - prepare your source codes

Annotate your sources to enable obfuscation in the build process:

import java.util.*;
import java.lang.*;
import java.io.*;

//
// you MUST include a custom annotation
// to enable the entire class or a single
// method obfuscation
//
@Obfuscate
class Ideone
{
    //@Obfuscate
    public static double calculateSD(double numArray[])
    {
        double sum = 0.0, standardDeviation = 0.0;
        int length = numArray.length;

        for(double num : numArray) {
            sum += num;
        }

        double mean = sum/length;

        for(double num: numArray) {
            standardDeviation += Math.pow(num - mean, 2);
        }

        return Math.sqrt(standardDeviation/length);
    }

    //
    // selective obfuscation strategies
    // can be applied for the entire
    // class or a single method (by
    // default all obfuscation strategies
    // are enabled when you use @Obfuscate
    // annotation alone)
    //
    //@Obfuscate(
    //  ints_math_crypt = true,
    //  dbls_math_crypt = true,
    //  string_split = true,
    //  crypt_strings = true,
    //  string_char_vault = true,
    //  rename_methods = false,
    //  rename_variables = true,
    //  shuffle_methods = true,
    //  array_int_crypt = true,
    //  array_double_crypt = true,
    //  array_char_crypt = true,
    //  array_string_crypt = true,
    //  mix_code_flow = true,
    //  ints_from_double_math = true,
    //  opaque_mixer_chain = true,
    //  complexify_booleans = true,
    //  try_finally_noise = true,
    //  ints_to_arrays = true,
    //  dbls_to_arrays = true,
    //  self_check = true
    // )
    public static void main(String[] args) {

        double[] numArray = { 1, 2, 3, 4, 5, 6, 7, 8, 9, 10 };
        double SD = calculateSD(numArray);

        System.out.format("Standard Deviation = %.6f", SD);
    }
}
And that's all! Just build your project like you did before. The obfuscation process is automated and fully invisible to you.

For more obfuscation features of the Maven plugin please refer to the official JObfuscator Maven Compiler documentation.

Tuesday, September 13, 2022

Java Source Code Obfuscator - JObfuscator

Obfuscate your Java source code & algorithms to protect it against reverse engineering analysis, cracking, and decompilation.

JObfuscator is a Java source code obfuscator to protect your work at the source code level. After compilation of the protected and obfuscated code - it will be extremely hard to reverse engineer the compiled bytecode, forget about Java decompilers!

Java Obfuscator - JObfuscator

Changes:

v1.10 - 09.08.2022
  • Fixed an error in the order of variable declarations when using obfuscation to change the linear path of code execution (thank you Yi Wu)
  • Automatically adding special annotation for IntelliJ IDE @SuppressWarnings(InstanceVariableMayNotBeInitialized) for the non-linear code path obfuscation

v1.09 - 06.02.2022
  • Fixed bug in annotation handling that caused string encryption obfuscation to work incorrectly
v1.08 - 19.10.2021
  • Fixed renaming methods within the same class
v1.07 - 17.08.2021
  • Improved integer to arrays obfuscation by generating multidimensional arrays e.g. int[][] var_3035 = { { 65535 }, { 01, 02, 0b0 } };
  • Improved doubles to arrays obfuscation by generating multidimensional arrays e.g. double[][][] O_ZzBf7_4tcNvh_c = { { { 2.8 } }, { { 1.3 } }, { { 0.06, 3.7, 65535.8 } } };

Saturday, July 31, 2021

Best Java Obfuscator?

Our Java Obfuscator - JObfuscator has been updated to include new Java obfuscation strategies.

Best Java Obfuscator - JObfuscator

Obfuscation engine history

v1.03 - 31.07.2021
  • Some integers were not extracted correctly for the integers to arrays obfuscation strategy
  • Multilevel obfuscation of extracted integers into the arrays (into a random number of double and integer arrays)
v1.02 - 30.07.2021
  • An integers to arrays obfuscation strategy, converts the integer values into double values to avoid deobfuscation by popular Java decompilers e.g. double[] var_2597 = new double[]{13.898355719807563D, 65535.73657403742D, ... };
v1.01 - 28.07.2021
  • A new obfuscation strategy. For each method, extract all possible integers from the code and store them in an array. It makes the analysis harder because it requires an indexed table lookup for every numeric value.

Client history


v1.01 - 28.07.2021
  • All clients (Windows, Linux) and SDKs (PHP & Python) updated to include the new obfuscation strategy /IntsToArrays

Sunday, July 25, 2021

JObfuscator Java Obfuscator

JObfuscator is a Java source code obfuscator. Secure your Java source code and algorithms.

Protect Java source code & algorithms from hacking, cracking, reverse engineering, decompilation & technology theft.


More information at:

https://www.pelock.com/products/jobfuscator


An online obfuscator interface:

https://www.pelock.com/jobfuscator/


Automate obfuscation with PHP & Python SDKs (with sources on GitHub)

https://www.pelock.com/products/jobfuscator/api


Windows & Linux clients (GUI & console version)

https://www.pelock.com/products/jobfuscator/download


Screenshots

JObfuscator console version

An obufscated and protected Java source code

Java obfuscator options panel

JObfuscator Java Source Code Obfuscator


Friday, January 1, 2021

Obfuscate AutoIt Scripts from Python code

If you would like to protect your AutoIt scripts from hackers and decompilation you might want to obfuscate their source code with an AutoIt Obfuscator.

Obfuscation protects the original AutoIt source code against analysis & reverse engineering. Unfortunately, AutoIt decompilation is easy with tools like aut2exe (try it yourself).

Obfuscation protects the AutoIt code against reversing, so even after decompilation the source code will stay safe from prying eyes, hackers, and competition.

Now it's possible to automate this process using Python 3 code with a dedicated Python 3 module:

https://pypi.org/project/autoitobfuscator/

Source code of this module along with usage examples is available at GitHub:

https://github.com/PELock/AutoIt-Obfuscator-Python

Sample usage example in Python:
#!/usr/bin/env python

###############################################################################
#
# AutoIt Obfuscator WebApi interface usage example.
#
# In this example we will obfuscate sample source with default options.
#
# Version        : v1.0
# Language       : Python
# Author         : Bartosz Wójcik
# Web page       : https://www.pelock.com
#
###############################################################################

#
# include AutoIt Obfuscator module
#
from autoitobfuscator import AutoItObfuscator

#
# if you don't want to use Python module, you can import directly from the file
#
#from pelock.autoitobfuscator import AutoItObfuscator

#
# create AutoIt Obfuscator class instance (we are using our activation key)
#
myAutoItObfuscator = AutoItObfuscator("ABCD-ABCD-ABCD-ABCD")

#
# source code in AutoIt v3 format
#
scriptSourceCode = 'ConsoleWrite("Hello World")'

#
# by default all options are enabled, both helper random numbers
# generation & obfuscation strategies, so we can just simply call:
#
result = myAutoItObfuscator.obfuscate_script_source(scriptSourceCode)

#
# it's also possible to pass script path instead of a string with the source e.g.
#
# result = myAutoItObfuscator.obfuscate_script_file("/path/to/script/source.au3")

#
# result[] array holds the obfuscation results as well as other information
#
# result["error"]         - error code
# result["output"]        - obfuscated code
# result["demo"]          - was it used in demo mode (invalid or empty activation key was used)
# result["credits_left"]  - usage credits left after this operation
# result["credits_total"] - total number of credits for this activation code
# result["expired"]       - if this was the last usage credit for the activation key it will be set to True
#
if result and "error" in result:

    # display obfuscated code
    if result["error"] == AutoItObfuscator.ERROR_SUCCESS:

        # format output code for HTML display
        print(result["output"])

    else:
        print(f'An error occurred, error code: {result["error"]}')

else:
  print("Something unexpected happen while trying to obfuscate the code.")

Python Obfuscator & Virtualizer

Python Obfuscator: protect the .py files you actually ship Python is honest to a fault. You hand someone a script and you have handed them ...